
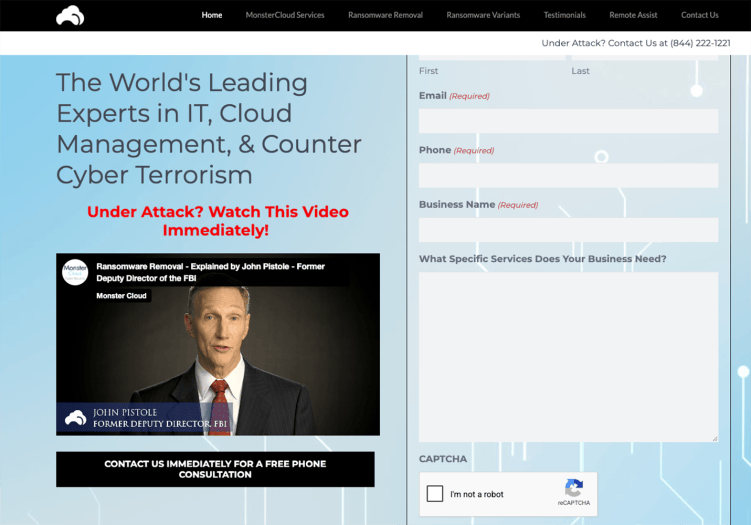
A Florida man named Zohar Pinhasi, previously investigated by ProPublica in 2019, now faces federal charges for allegedly defrauding clients of his ransomware data recovery firm. The Justice Department states that Pinhasi misled customers, claiming he could decrypt files without ransom payments, when he actually paid ransoms and charged clients substantial fees.
This indictment aligns with ProPublica’s 2019 findings detailed in an article titled “The Trade Secret.” The report exposed how Pinhasi’s firm, MonsterCloud, exploited ransomware victims, harming them a second time by misleading them about not paying ransoms. U.S. Attorney Joseph Nocella emphasized in an October press release that Pinhasi’s actions re-victimized clients for his own profit. The prosecution against ransomware attackers and those capitalizing on such criminal activities is strong.
The 2019 article highlighted the growing threat of ransomware on a global scale affecting governments, schools, and businesses. Hackers typically demanded ransom in cryptocurrencies like bitcoin, complicating traceability. ProPublica’s investigation showcased how entities like MonsterCloud and insurance companies contributed to this extortion cycle.
Despite Pinhasi’s claims to ProPublica in 2019 that MonsterCloud did not specify recovery methods, the firm’s popularity among local law enforcement pointed to a belief in its non-ransom policies. However, many clients and experts revealed instances suggesting otherwise. Over time, Pinhasi is alleged to have collected over $19 million from clients while paying out $8 million in ransoms.
Pinhasi, operating under the alias Zack Green, reportedly contacted up to 30 clients daily, employing around 20 individuals with global contacts. In some cases, clients were charged massive sums compared to the ransom paid, such as one instance where a $150,000 fee was billed for an $8,200 ransom payment.
If convicted, Pinhasi could face up to 20 years in prison. An FBI official condemned his deceptive practices, highlighting the breach of trust in crisis situations. Despite ProPublica’s prior findings, the Justice Department’s stance did not address that FBI associate John Pistole was linked to MonsterCloud in promotional content. Pistole, who was involved with MonsterCloud’s “Cyber Security Advisory Council,” acknowledged receiving payment through a speaker’s bureau and the reality of ransom payments in data recovery.
Though MonsterCloud marketed itself with claims of proprietary technology and strong law enforcement ties, the indictment does not specifically mention Pistole. His comments in 2019 supported the industry’s reliance on ransom payments for decrypting files.